-
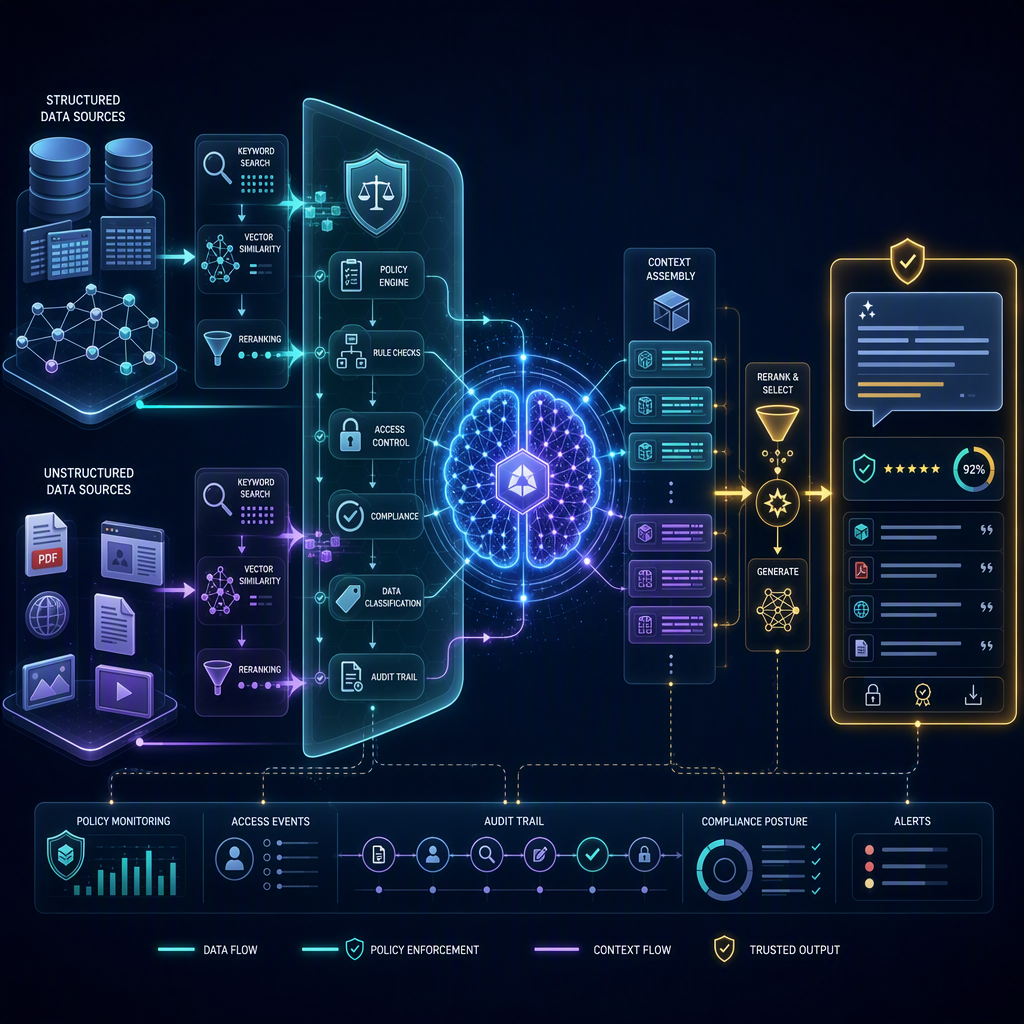
Policy-Aware Hybrid Retrieval-Augmented Generation (HRAG-PA): A Knowledge-Aware AI Framework for Cybersecurity Governance
Cybersecurity governance depends on understanding and applying complex regulatory frameworks including ISO/IEC 27001, NIST CSF 2.0, GDPR, and HIPAA and many others. Often these frameworks are sector specific, difficult to read, and complicated to apply. To simplify the implementation and comprehension of these models within firms this post proposes to leverage Large Language Models…