-
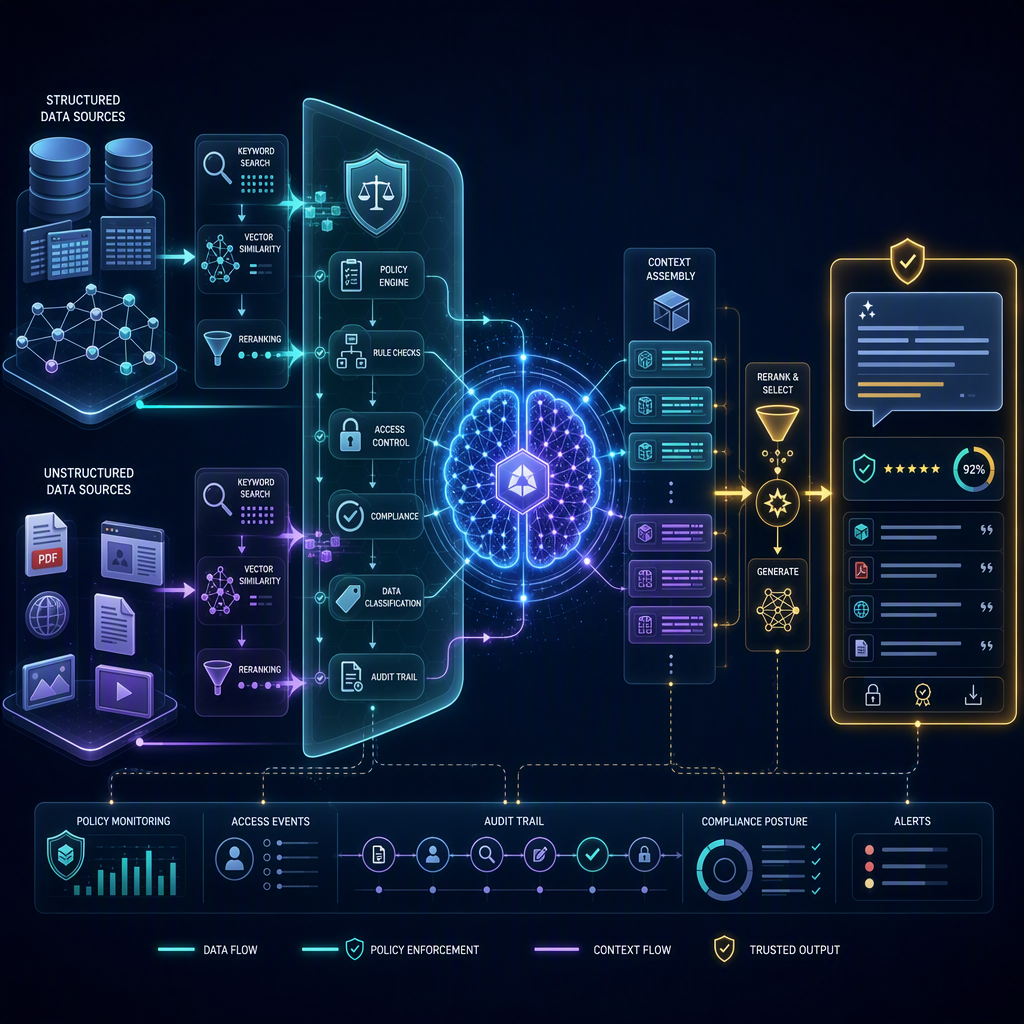
Policy-Aware Hybrid Retrieval-Augmented Generation (HRAG-PA): A Knowledge-Aware AI Framework for Cybersecurity Governance
Cybersecurity governance depends on understanding and applying complex regulatory frameworks including ISO/IEC 27001, NIST CSF 2.0, GDPR, and HIPAA and many others. Often these frameworks are sector specific, difficult to read, and complicated to apply. To simplify the implementation and comprehension of these models within firms this post proposes to leverage Large Language Models…
-

Reflections on The Atlantic Council’s Cyber912 Strategy Challenge
By Ethan Dettman and Halima Binte Islam Special thanks to the Hume Center for National Security and Technology for providing financial support to our team. Introduction During the first weekend of March, we had the opportunity to travel to Washington, D.C. to compete in the Cyber912 Strategy Challenge. Hosted by the Atlantic Council, the event saw 40 teams from 36 schools…